Reading the Fine Print on Your DNA: What Americans Actually Control Over Their Genomic Information
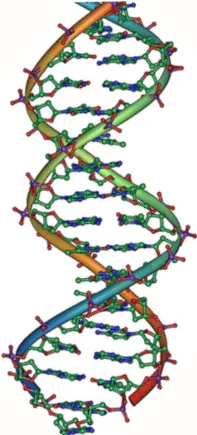
Photo: Jerome Walker, Dennis Myts, Public domain, via Wikimedia Commons
A saliva sample mailed to a testing company can feel like a simple transaction: you send DNA, you receive an ancestry chart or a carrier report. What happens afterward is considerably murkier. In the United States, control over genomic data is determined not by one comprehensive law but by an overlapping set of federal statutes, state measures, and—critically—the terms of service a person clicked through in under two minutes.
For patients, research participants, and consumers, understanding that patchwork has become a practical necessity.
Why No Single Law Governs Your Genome
The most common misconception is that HIPAA protects all health information, including genomic data. In reality, HIPAA applies only to covered entities—health plans, healthcare clearinghouses, and certain providers. A direct-to-consumer testing company selling kits online generally falls outside HIPAA's reach unless it operates through covered healthcare channels.
The Genetic Information Nondiscrimination Act of 2008, or GINA, is likewise narrower than many assume. GINA prohibits discrimination by health insurers and employers based on genetic information, but it does not regulate who may access or sell your data, and it offers no protection in life insurance, long-term care insurance, or disability insurance underwriting.
Into that gap have stepped state legislatures. California, Florida, Utah, and more than thirty other states have enacted genetic privacy statutes of varying strength. Some require explicit, opt-in consent before genetic data may be shared with third parties; others permit de-identification and sale with minimal friction. A resident of one state may enjoy protections a resident of a neighboring state lacks entirely.
The Contract Layer: Terms of Service as De Facto Privacy Law
For consumer genomic data, the operative legal document is often the terms of service and privacy statement agreed to at purchase. These contracts govern whether a company may retain your sample, share de-identified data with pharmaceutical partners, or license datasets for research.
Most major consumer companies now allow customers to opt in or out of research data sharing, and many permit account deletion and sample destruction on request. But the details matter. Some agreements distinguish between de-identified and identified data; others reserve broad rights to use aggregated information even after an account closes. Reading these documents is tedious, but it remains the single most consequential step a consumer can take.
Scenario: An Acquisition Changes Hands
Consider a plausible sequence of events. A consumer genomics company accumulates data from millions of customers, then faces financial distress and is acquired. The acquiring entity inherits not only the platform but the contractual rights to use the underlying dataset—rights defined by terms of service that may have changed multiple times over a decade.
Customers' remedies at that point are limited. Those who opted out of research sharing generally have stronger footing; those who consented to broad data use may find their data transferred along with the rest of the company's assets. The episode illustrates a structural truth: consent given years ago binds data to whatever entity holds it today, under whatever terms were in force at the time.
Scenario: The Research Volunteer
A different calculus applies in academic research. Under the Common Rule, federally funded research requires informed consent, and NIH-funded genomic studies are subject to specific data-sharing expectations. Participants typically receive a plain-language consent form describing whether data will be deposited in controlled-access repositories, whether they may withdraw, and whether they will be re-contacted.
Yet even careful consent forms cannot fully anticipate the future. Re-identification risks grow as databases expand, and family members—who share much of a person's genome—never signed anything at all.
A Checklist for Evaluating Consent and Contracts
The Institute recommends that patients and participants ask five questions before sharing genomic data:
- Who holds the data, and under which legal framework? Determine whether the entity is a covered entity under HIPAA or governed by a state statute.
- Is consent opt-in or opt-out? Default settings shape outcomes for most people.
- Can I withdraw, and what does withdrawal actually remove? Deleting an account is not always the same as removing data from distributed research datasets.
- What happens on sale, merger, or bankruptcy? Look for explicit language about data transfer.
- Are there protections for relatives? Genomic data is inherently familial; few agreements address this directly.
Toward Clearer Defaults
No pending federal legislation would create a comprehensive genomic privacy regime, though proposals have been introduced in recent Congresses. In the meantime, the burden of diligence falls on individuals—patients reading consent forms, consumers skimming terms of service, participants weighing altruism against uncertainty.
That is not an argument against participation in genomic research, which remains essential to medical progress. It is an argument for clearer contracts, stronger default protections, and a national conversation about whether the current patchwork adequately serves the people whose DNA makes the entire enterprise possible.